Mission
To protect organisations with a proactive approach to cybersecurity, combining advanced technology with high-level human expertise.
home / company
about us
Exploit Finder is the web penetration testing and vulnerability assessment service of Cyber Advisory LLC, a cybersecurity company founded by a group of researchers with over thirty years of experience.
what we do
We provide security assessments, consulting and security testing to protect websites, applications and digital infrastructure. Every assessment ends with a report that both the technical team and management can read and, when needed for tenders, clients or auditors, a signed attestation letter.
Our mission is to turn security from a cost into a competitive advantage.
mission, vision, values
To protect organisations with a proactive approach to cybersecurity, combining advanced technology with high-level human expertise.
A safer digital ecosystem, in which every company operates with a solid security posture that is verified over time.
Integrity, transparency, continuous innovation and a constant commitment to technical excellence and client satisfaction.
the founder
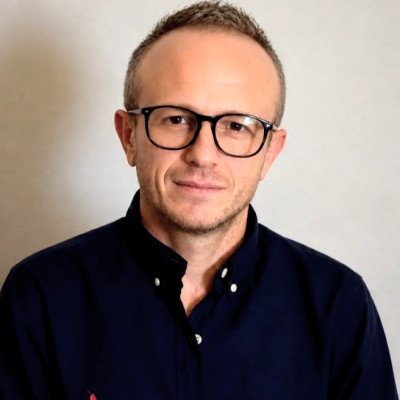
Chieppa Vincenzo, known in the international security community as procode701, has built his reputation on years of contributions to the security of some of the world's most prominent platforms, including Uber, Facebook, Google and Microsoft.
His experience spans advanced penetration testing, vulnerability research, security architecture and strategic consulting for enterprise organisations.
In over twenty years of work he has trained and led security teams in several countries and developed the proprietary methodologies on which the Exploit Finder platform is based. He takes part in public bug bounty programmes on HackerOne, where his validated reports have been acknowledged and rewarded.
expertise
Tests on web and mobile applications, APIs and network infrastructure, with methodologies aligned to international standards.
In-depth analysis of vulnerabilities, with detailed reports, risk prioritisation and operational remediation plans.
Security audits aligned to ISO 27001, NIST, GDPR, SOC 2 and Cyber Essentials, with documentary evidence.
Support in defining security strategy, IT governance and a roadmap for continuous improvement.
Continuous research into new vulnerabilities, attack techniques and defensive tools.
how we work
No test without a signed declaration and a verified domain.
The system does not leave the signed scope, even if the model proposes it.
Every confirmed vulnerability is reproduced and assessed by a person.
company
Registered office: 300 SE 5th Ave, Suite 7150, Boca Raton, FL 33432, USA.
Request a web security assessment, or a quote for multiple domains, enterprise or NIS2. We reply with a proposal tailored to your scope.